ML-KEM Algorithm vs RSA: Understanding the New Quantum-Resistant Standards
The ML-KEM algorithm represents the biggest fundamental shift in enterprise public key cryptography in over four decades. For years, organizations built their entire Public Key Infrastructure (PKI) around RSA integer factorization mathematics, trusting that classical supercomputers could never process the calculations required to crack a 2048-bit or 4096-bit private key.
That mathematical protection faces an imminent existential threat. The rapid development of Cryptographically Relevant Quantum Computers (CRQCs) running Shor’s algorithm will eventually solve integer factorization in minutes, rendering conventional RSA keys instantly useless. To prevent hostile actors from harvesting encrypted enterprise traffic today to decrypt tomorrow, the National Institute of Standards and Technology (NIST) finalized FIPS 203, establishing the ML-KEM algorithm as the official global standard for quantum-safe key encapsulation.
Transitioning enterprise architecture from legacy RSA to lattice-based cryptography requires engineering leadership to rethink fundamental assumptions about key sizes, protocol handshake mechanics, and endpoint performance. Preparing your infrastructure for post-quantum reality demands addressing three structural shifts.
Core Shifts Moving from RSA to the ML-KEM Algorithm
-
Mathematical Structural Disruption: RSA relies on the computational difficulty of factoring giant prime numbers, whereas the ML-KEM algorithm relies on the Module Learning-With-Errors (MLWE) lattice problem.
-
Packet Size and Memory Explosion: Replacing compact RSA keys with quantum-safe key encapsulation mechanisms increases public key and ciphertext payloads by orders of magnitude.
-
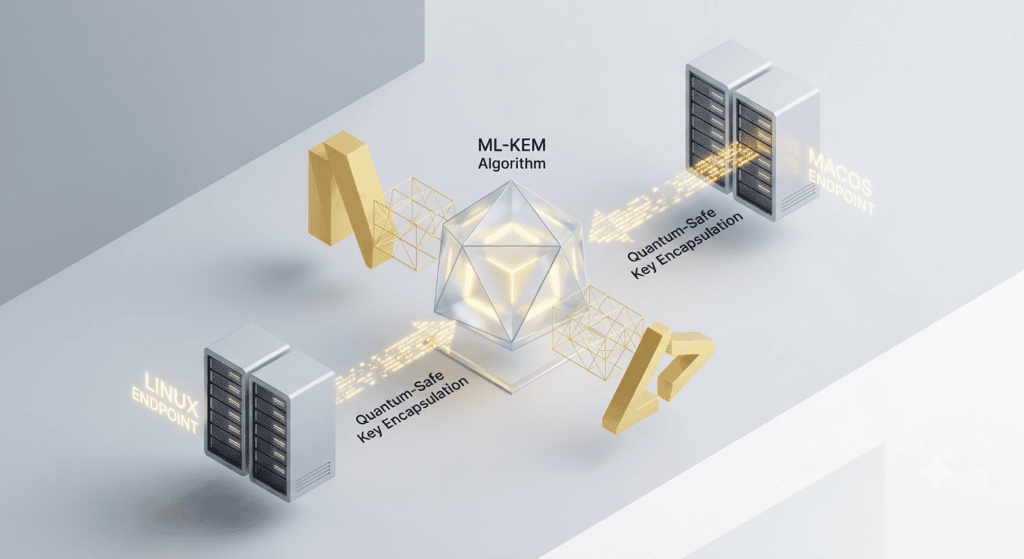
The Mixed-OS Infrastructure Migration Burden: While modern operating systems slowly add post-quantum ciphers, extending these massive cryptographic payloads to non-Windows platforms like Linux and macOS creates critical deployment bottlenecks.
The Mathematical Collapse of Prime Factorization
RSA derives its mathematical strength from a simple computational asymmetric principle: multiplying two large prime numbers together takes milliseconds, but finding those original prime factors from the resulting product takes classical supercomputers millennia. Shor’s algorithm completely dismantles that security model by leveraging quantum superposition to evaluate factor probabilities simultaneously across thousands of logical qubits. Once quantum hardware reaches fault-tolerant scale, RSA offers zero mathematical defense.
[ RSA Model ]     Factorization Problem ──► Solvable by Quantum Shor's Algorithm ──► Broken Security
[ ML-KEM Model ]  Module-Lattice (MLWE) ──► High-Dimensional Vector Noise      ──► Quantum-Safe
In contrast, the ML-KEM algorithm (standardized from CRYSTALS-Kyber) relies on the inherent difficulty of solving algebraic lattice problems in high-dimensional vector spaces. Instead of searching for prime factors, an attacker must identify a specific grid point inside a multi-dimensional lattice hidden behind intentional mathematical noise. Because neither classical nor quantum algorithms can solve these Module Learning-With-Errors problems efficiently, lattice cryptography provides robust, long-term confidentiality against eavesdropping.
Payload Expansion and Network Overhead
Adopting quantum-safe key encapsulation forces network architects to accept a massive expansion in cryptographic payload sizes. Under standard RSA-2048, an enterprise web server transmits a public key roughly 256 bytes long. When migrating to the baseline post-quantum parameter—ML-KEM-768—that public key size balloons to 1,184 bytes, accompanied by an additional 1,088-byte ciphertext during the key exchange.
These expanded payload sizes fundamentally alter network traffic dynamics across your enterprise network:
-
TCP Packet Fragmentation: Larger key exchange payloads easily exceed standard 1,500-byte Maximum Transmission Unit (MTU) network limits. This forces single TLS handshakes to split across multiple IP fragments, increasing dropped-packet risk over unreliable links.
-
Increased Handshake Latency: Fragmented network packets add extra round-trip times (RTT) during session negotiation, degrading client-server responsiveness across high-velocity applications.
-
Memory Footprint Escalation: Endpoints processing thousands of concurrent secure connections must allocate significantly more RAM to store lattice-based key states during decryption operations.
As we explored in our analysis of why the traditional 90-day TLS certificate is already obsolete, compounding operational velocity with larger payload demands quickly breaks legacy deployment pipelines. Security teams cannot simply swap out keys; they must overhaul their underlying network tooling to handle post-quantum data volume.
Navigating Cross-Platform Post-Quantum Migration
The primary hurdle for enterprise migration does not involve updating core Windows Active Directory domain controllers. Microsoft continues building native post-quantum primitives into Windows Server ecosystems. Instead, the operational bottleneck emerges across your heterogeneous non-Windows environment.
Enterprise Linux hosts, cloud container nodes, and corporate macOS workstations run a fragmented array of cryptographic libraries (OpenSSL, GnuTLS, CommonCrypto). Manually provisioning, testing, and updating lattice-based keys across these disparate endpoints introduces massive administrative friction. If an engineer manually deploys an incorrectly configured hybrid RSA/ML-KEM certificate to a production Linux host, that node suffers silent connection drops, broken handshake negotiations, or severe performance degradation.
Attempting to track these shifting algorithm standards and short validity windows manually accelerates security team burnout. As regulatory mandates like CA/B Forum Ballot SC-081v3 enforce a mandatory 47-day certificate lifespan, combining hyper-frequent renewals with complex post-quantum key configurations renders manual administration entirely unworkable.7
Streamlining Post-Quantum PKI with Revocent
Surviving the transition from RSA to the ML-KEM algorithm does not require buying a bloated, expensive discovery tool that merely scans your network to tell you that legacy keys exist. Instead, enterprise security teams require direct, reliable execution at the endpoint level to manage certificate enrollment and renewal automatically.
CertAccord Enterprise solves the cross-platform post-quantum transition by bringing native Microsoft Active Directory Certificate Services (ADCS) auto-enrollment to Linux and macOS environments. Rather than forcing your engineering team to manually generate CSRs, convert key formats, or manage complex custom scripts across open-source hosts, CertAccord acts as an automated agent.
CertAccord bridges your non-Windows systems directly to your trusted Windows PKI infrastructure. As your organization upgrades its internal CA templates to support post-quantum standards, CertAccord automatically manages key generation, enrollment, installation, and rotation on your Linux servers and macOS endpoints behind the scenes.
In conclusion, quantum computing will make legacy RSA obsolete sooner than most enterprise roadmaps anticipate. By implementing CertAccord Enterprise across your mixed-OS infrastructure today, you insulate your network from complex cryptographic shifts, maintain continuous compliance, and empower your security staff to focus on strategic operational defense.